Kaspersky's Global Research and Analysis Team (GReAT) has uncovered a scam targeting tourists who are applying for a Schengen visa. They receive phishing emails allegedly sent on behalf of an EU migration authority. Under the threat of additional checking procedures at the border, the scammers urge tourists to visit a fake website and submit a “migration declaration” which prompts users to share personal information or passport scans. The malicious campaign targets those who speak English, Turkish, Arabic, and other languages.
The phishing emails claim that, under new rules for crossing the borders of Schengen Area countries, all tourists are required to submit a digital migration declaration five working days before entering. To do so, they are instructed to register on a fake website imitating the European Union’s Entry/Exit System (EES), which did indeed begin operating in April 2026.
The email claims that if the application is not completed, tourists may face additional checks during border control or even be temporarily denied entry. To lull tourists into a false sense of security, the scammers reassure that the migration authorities never ask for payment details by email and that migration information should only be provided through the “official EU tourist portal for the Schengen Area”.
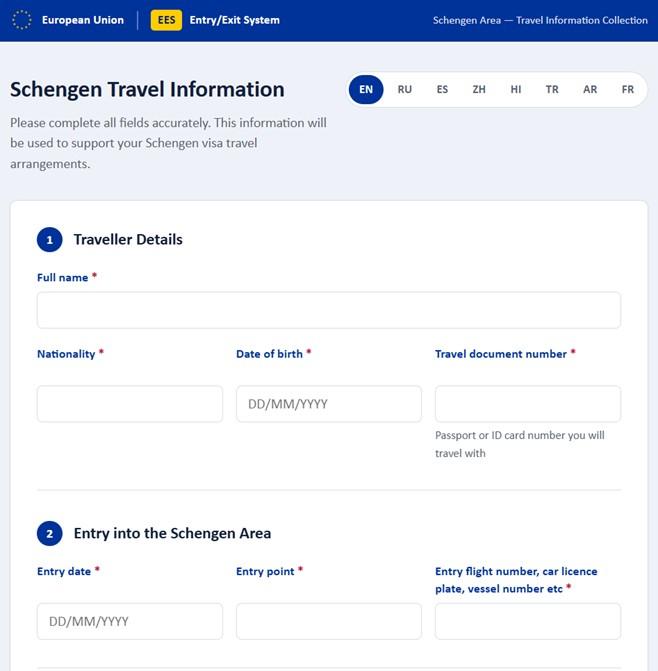
To make the website appear legitimate, the fake site uses European Union imagery and is available in several languages, including English, Turkish, Arabic, Chinese, Spanish and others. Tourists are asked not only to provide their personal details, but also information about accompanying travelers, to enter their dates of entry into and departure from the Schengen Area, and upload scans of their passports. The information collected through this fake website could potentially be used by the perpetrators to contact victims by phone and attempt to obtain further personal information or financial details.
“Cybercriminals rely on creating a sense of urgency. They know travelers may have spent weeks preparing their visa applications and fear problems at the border. That's the reason why such emails can make recipients drop their guard, especially when the fake site looks convincing, with a multilingual interface and a design that resembles the official EU portal. Travelers should remember that they do not currently need to register for the EES online in advance. We also advise to check the sender’s address and verify any new requirements directly with the relevant consulate or visa center. Don’t click links in unexpected emails or upload passport scans or other documents to third-party websites,” comments Georgy Kucherin, Senior security researcher at Kaspersky GReAT.
Experts at Kaspersky share tips to help avoid falling victim to such travel scams:
· Carefully check websites before entering any information. Look out for typos, extra characters, or unusual domains.
· Do not trust links or attachments received by email. Before opening an attachment, double-check the sender.
· To access the Internet while abroad, use an eSIM – you can purchase one, for example, through Kaspersky eSIM Store. Digital SIM cards are best activated through official apps, eliminating the need to obtain physical SIM cards.
· Use a reliable security solution to protect your devices, privacy, and identity, such as Kaspersky Premium.